Cybersecurity
A Security Baseline for a Small Office Network
9 min read
Small offices rarely need an expensive security program first. They need a known inventory, sensible network boundaries, maintained devices, recoverable data, and a clear response when something looks wrong.
Know what is connected
List routers, switches, access points, printers, cameras, servers, laptops, phones, and cloud-managed devices. Record the owner, location, purpose, update method, and whether the default password was changed. Unknown devices are unmanaged risk.
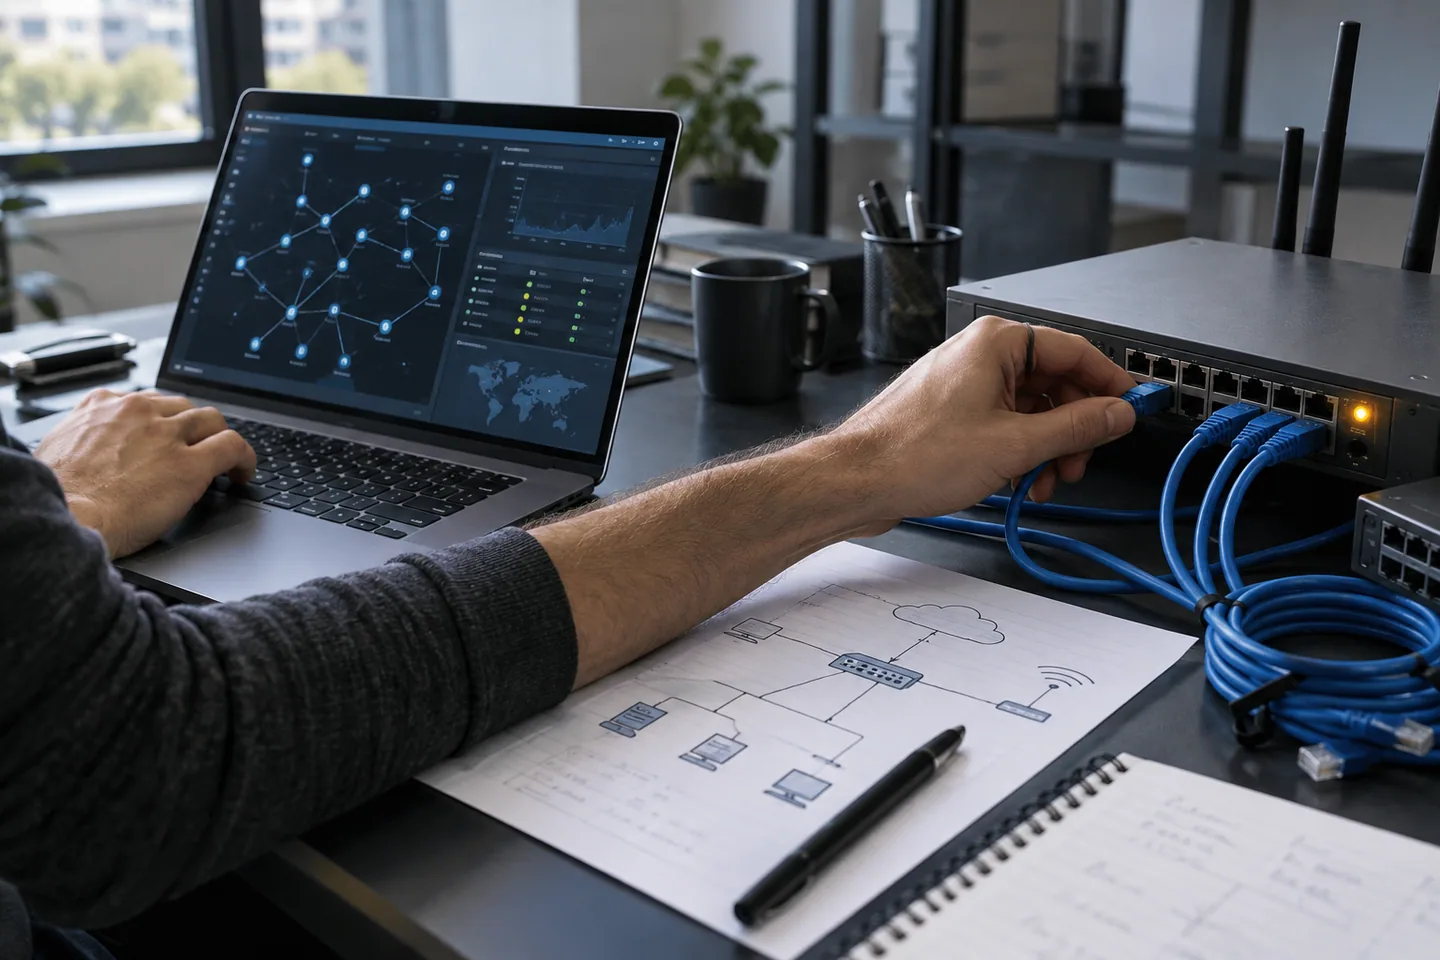
Draw a simple network map. Separate staff, guest, payment, camera, and infrastructure traffic where the equipment allows it. Guest users should not be able to discover office printers or administration pages.
- Change default administrator credentials
- Disable unused remote-management services
- Back up router and firewall configuration
- Keep management interfaces off the guest network
Harden identities and endpoints
Turn on multi-factor authentication for email, finance, hosting, and administration accounts. Remove access promptly when someone leaves. Device updates, disk encryption, screen locks, and endpoint protection should be baseline settings rather than personal choices.
Use a password manager and unique credentials. Shared accounts remove accountability; if one must exist, document ownership and rotate it when team membership changes.
- Use least privilege for daily accounts
- Review administrator membership monthly
- Patch browsers, operating systems, and network firmware
- Block macros and unknown software where practical
Prepare for recovery
Backups are useful only after a restore test. Keep at least one protected copy that ordinary ransomware or an accidental deletion cannot immediately reach. Record how long critical work can stop and which systems must return first.
Give staff one simple reporting path for suspicious messages, lost devices, or unusual login prompts. Early reporting is more valuable than blame.